





For small and medium sized organizations, cybersecurity is becoming a business imperative, a new Kaspersky survey reveals. 71% of companies operating within a supply chain fail to meet all the IT security requirements set by their partners. As a result of this non-compliance, the vast majority of businesses face serious repercussions, ranging from contract delays to tender disqualification and emergency spending. SMBs that deploy advanced cybersecurity solutions are more likely to achieve full compliance and mitigate business losses.
Supply chain attacks, which exploit vulnerabilities in third-party software, have recently emerged as a top threat to large enterprises. In response, corporations are raising security standards for suppliers and partners, putting new pressure on SMBs across the supply chain. To help smaller companies adapt to new market demands, Kaspersky examined the current state of organizations’ security compliance and explains how cybersecurity solutions can both cover SMBs’ needs and ease the compliance process.
The study reveals that nine out of ten (90%) of SMBs involved in supply chains had to satisfy any IT security requirements of their customers or partners. At the same time, less than one third (29%) of organizations managed to meet all the proposed requirements. The ability to meet all security requirements is linked with the IT security level of companies. Only 3% of companies describing their level of IT security as low (basic protection only implemented) managed to meet all requirements, while this share among organizations using advanced solutions, such as EDR, XDR, SIEM, reached 44%.
Among SMBs that are already a part of any supply chain, 71% managed to only partially meet IT security requirements from a partner. One of the toughest criteria that led to non-compliance was obtaining IT security certifications: 26% of respondents failed to meet it. In addition, sharing and revising incident response plans (26%), implementing advanced IT security solutions (26%) and conducting regular third-party penetration testing or security audits (25%) were the most frequent requirements that surveyed companies did not satisfy.
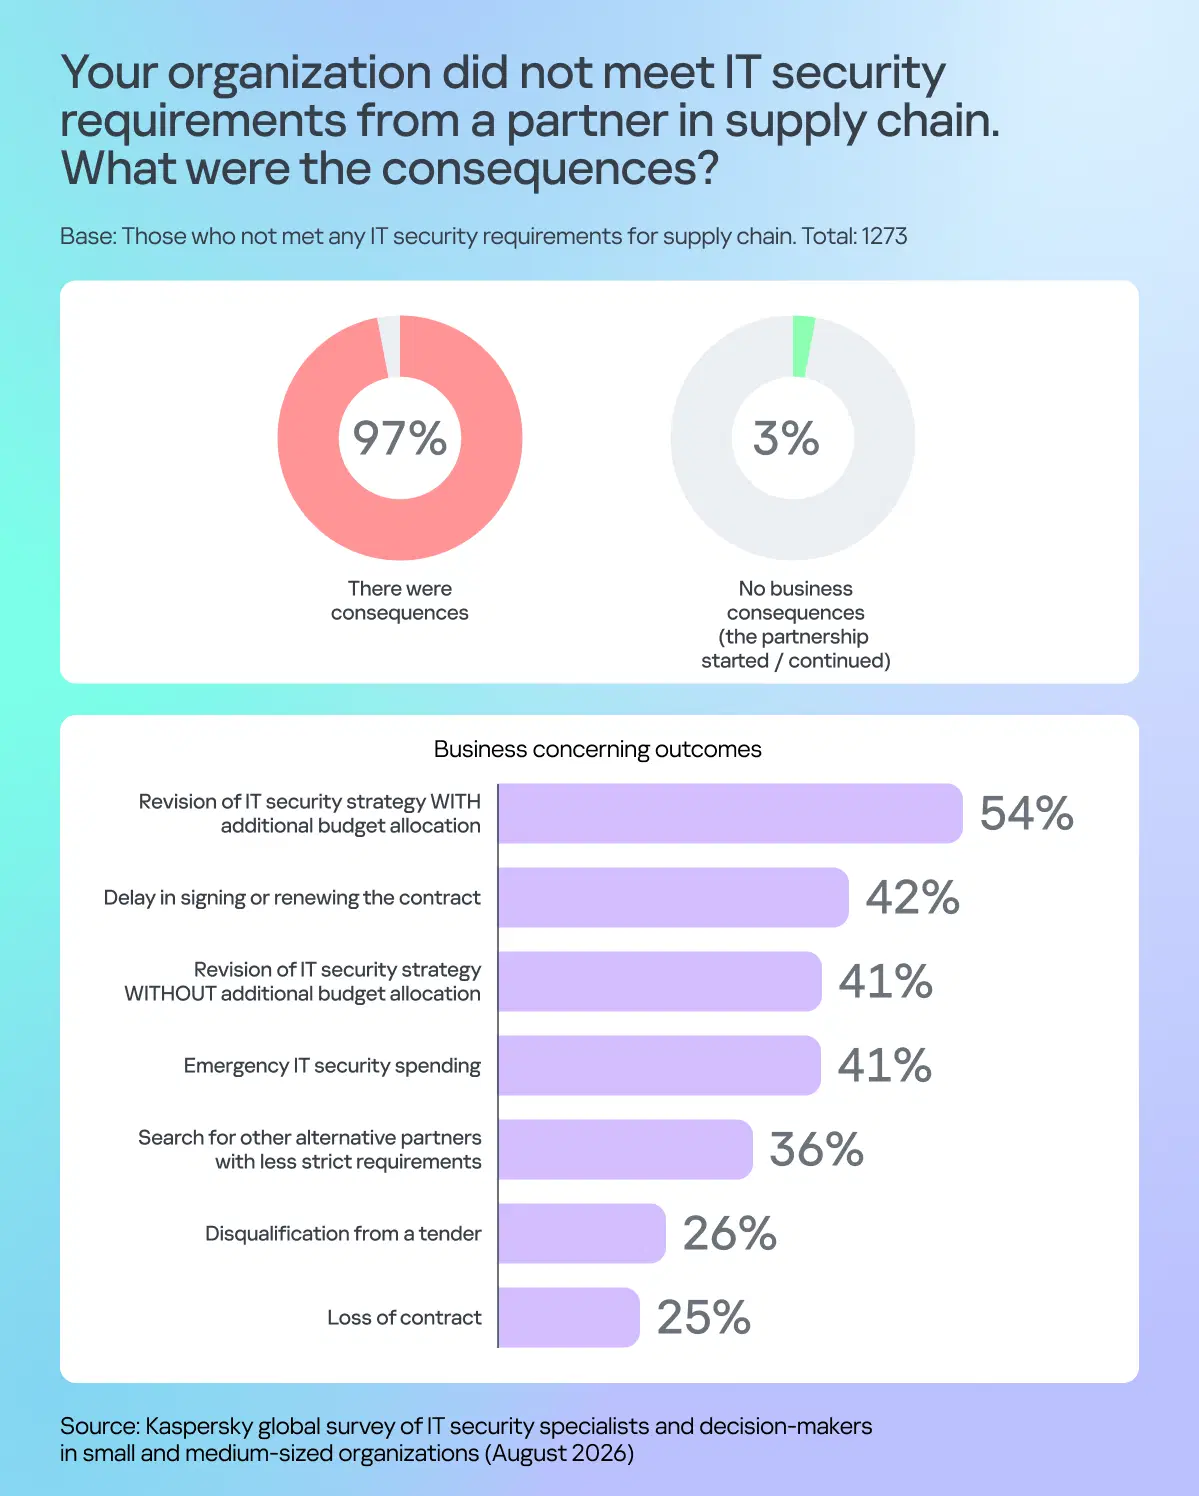
In terms of the non-compliance impact, only 3% of SMBs that did not meet any IT security requirements could state they managed to continue or start partnership without any consequences. The remaining 97% admit that failing to meet any security requirements led them to business concerning outcomes. The majority of companies were forced to revise their IT security strategy and, in most cases, revision came with additional budget allocation (54%). Loss of revenue opportunities also affected a significant part of organizations: 42% faced contract delays, 26% were disqualified from a tender and quarter (25%) just lost contract.
“Cybersecurity advancement is becoming more and more important for SMBs. Large companies as usual were pioneering in technologies and now they take smaller companies with them. On the bright side, business is becoming more protected, but the transition phase, however, can be painful for growing companies due to insufficiency of expertise and small resources. SMBs and mid-market organizations are the main heroes for Kaspersky right now. We see that these organizations need support from leading vendors, and we are developing our solutions specifically to fit the needs of smaller companies.” – comments Zoya Gurevich, senior product manager at Kaspersky. “For SMBs, improving cybersecurity starts with addressing technical vulnerabilities and everyday security risks. Automated and easy-to-handle tools help identify weaknesses, monitor activity at the endpoint level and protect communication channels, e.g. corporate emails. Combined with practical employee training, these measures help reduce the risk of incidents, maintain long-term business continuity and meet the security requirements of partners and customers”.