Gartner Identifies Top Five Actions for CISOs to Take by End of 2026
“AI-augmented cyberattacks, AI safety debates and emerging quantum computing risks create persistent uncertainty across the enterprise,” said Christopher Mixter, VP Analyst at Gartner. “Cybersecurity leaders have a career-defining opportunity to guide executive decision making through this period of accelerating technological disruption.
“By taking a proactive approach, leaders can build lasting organizational trust, moving beyond response and recovery to deliver true cybersecurity assurance.”
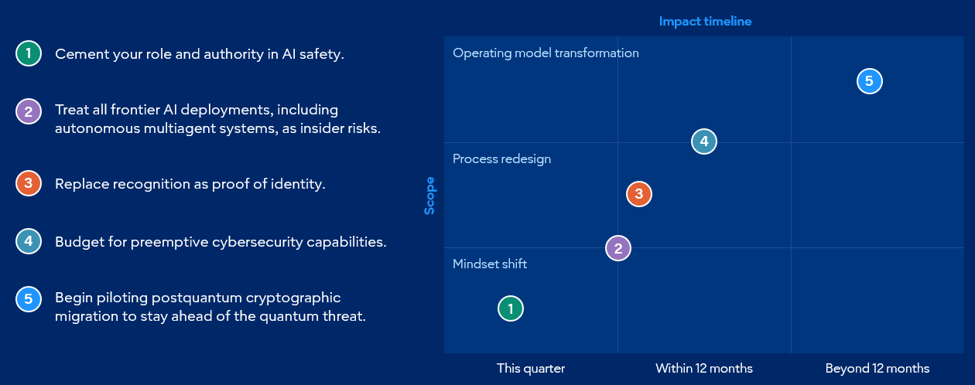
Gartner recommends cybersecurity leaders take five specific actions in the fourth quarter of 2026 and beyond (see Figure 1).
Figure 1: Cybersecurity Decisions to Make in Q4 2026
Source: Gartner (September 2026)
Securing AI infrastructure and understanding the interaction between models and harnesses is more important than the safety of the model itself. CISOs can guide other C-suite leaders past hype and drive internal governance and tactical implementation. CISOs are becoming the defacto authority on AI safety in the enterprise, creating a significant opportunity for role evolution and executive leadership.
Treat All Frontier AI Deployments as Insider Risks
Fifty-four percent of organizations have no defined approach to limit AI agent access, or rely on predefined human access, according to a Gartner survey in 297 cybersecurity leaders in the second quarter of 2026. An AI system does not need to achieve artificial general intelligence capabilities to create significant cyber risk. It simply needs the ability to impact enterprise operations.
CISOs should govern autonomous multiagent systems based on action privileges rather than model intelligence and safeguard agentic workflows using guardian agents to constrain blast radiuses.
Replace Recognition as Proof of Identity
Deepfake threats are now mainstream. To protect the enterprise, CISOs must drive process redesign across the enterprise that discard recognition as an acceptable basis for decision or action authorization. Secure the organization’s online presence and brand by building a multi-layered approach that augments deepfake detection technology with contextual signals, additional authentication layers and checks on content provenance.
Budget for Preemptive Cybersecurity Capabilities
AI is drastically reducing the time and skill required for adversaries to exploit organizational weaknesses. Reflecting this shift, 76% of CISOs ranked AI-driven discovery of cyber vulnerabilities among their top 10 emerging risks in a survey of over 300 enterprise risk leaders in the second quarter of 2026.
“Detection and response capabilities are no longer sufficient,” said Luis Castillo, Senior Director Analyst at Gartner. “Organizations should prioritize preemptive cybersecurity capabilities such as automated moving target defense, advanced obfuscation, deception and predictive threat intelligence, to gain a measurable advantage over attackers.”
Being Piloting Postquantum Cryptographic Migration
Gartner predicts that organizations that do not begin piloting postquantum cryptographic (PQC) by 2027 will face at least 200% higher costs for their full migration. The survey of CISOs found that more than half (51%) have not yet begun any PQC-related activities.
“Postquantum readiness requires a comprehensive cybersecurity operating model transformation, not just a technical upgrade,” said Mixter. “Quantum threats, including harvest now, decrypt later (HNDL) and harvest now, forge later (HNFL), are capturing executive attention and demanding immediate action. Cybersecurity leaders must prepare today to protect sensitive data and ensure long-term cryptographic resilience.”

 should take by the end of 2026 to combat accelerating technological disruption.)